Security as a managed service
Cyber threats evolve every day and demand skills, tools and constant attention that are not always feasible to maintain in-house.
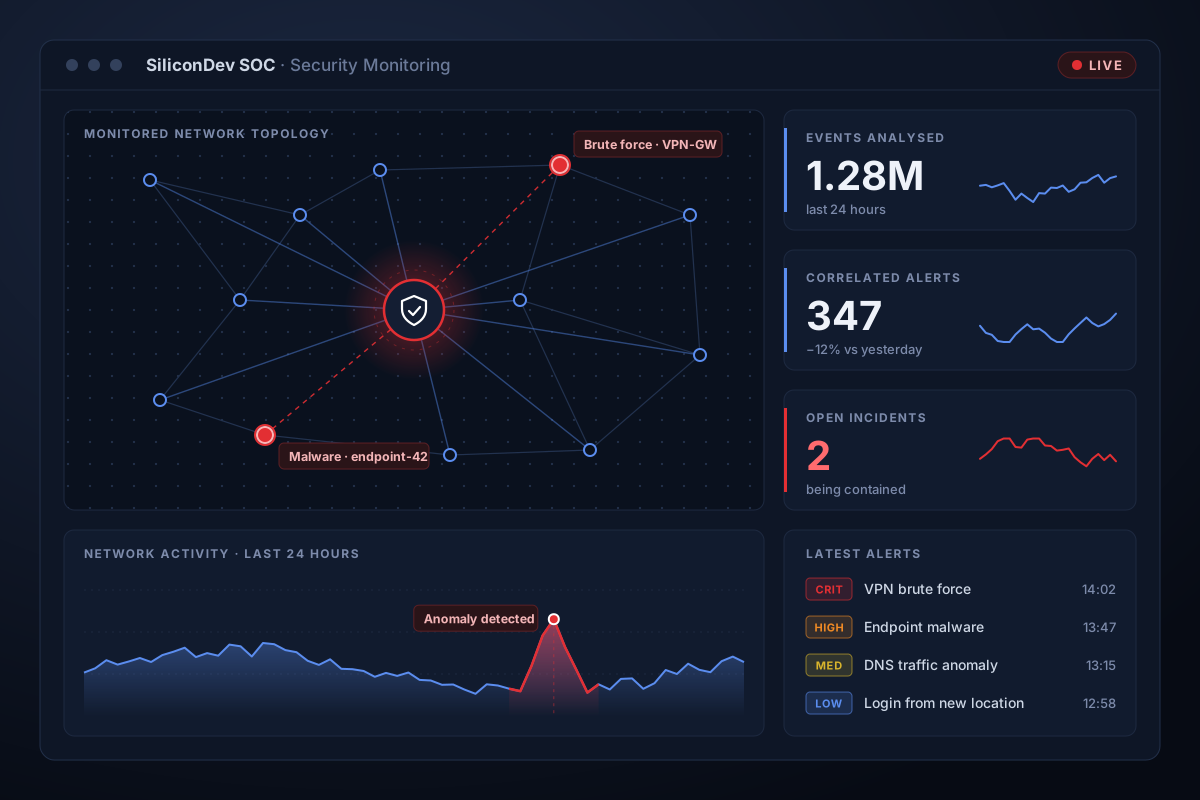
The SiliconDev Security Operations Center helps companies protect their IT infrastructure: we collect and correlate security events from networks, servers, endpoints and cloud services, identify anomalous behaviour and act quickly to contain incidents.
A service that integrates with your existing systems and adapts to the size and sector of each Client, combining technology with the experience of our cybersecurity specialists.
Every relevant event is analysed, classified by severity and, when needed, handled according to escalation procedures agreed with the Client, with full visibility of what is happening.
Our services
Continuous monitoring
Centralised collection and correlation of logs and security events through a SIEM platform, analysed by our security analysts.
Threat Detection
Detection rules, behavioural analytics and threat intelligence to promptly identify attacks, intrusions and suspicious activity.
Incident Response
Incident handling from first alert to recovery: analysis, containment, remediation and a final report with recommended actions.
Vulnerability Management
Regular scans of systems and applications, risk-based classification of vulnerabilities and support in planning remediation.
Compliance
Support in meeting security and data protection regulatory requirements, such as the NIS2 Directive and the GDPR.
Reporting
Regular reports and clear dashboards on security posture, detected events and risk trends, designed for both technical teams and management.
How we work
- AssessmentWe analyse your infrastructure, processes and key risks to define the scope of the service.
- OnboardingWe connect your data sources to the SOC and configure detection rules and escalation procedures.
- MonitoringOur analysts watch over events, filter out false positives and flag what really matters.
- ResponseIf an incident occurs, we act according to the agreed procedures to limit its impact.
- ImprovementRegular reports and reviews to strengthen your security posture over time.
Want to assess your company’s security posture?
Get in touch: one of our specialists will help you find the service that best fits your needs.
Contact us